Every AI meeting assistant has a data-protection problem that most other AI tools don't: it processes the words of people who never chose it. The prospect on a sales call, the candidate in a recruitment interview, the external partner in a project review – none of them accepted the vendor's terms, yet their voices, statements, and often personal details end up in a transcript, a summary, and possibly a third-party language model.
What gets said in those meetings raises the stakes further. Conversations regularly cover contract terms, salary decisions, health-related accommodations, or strategic plans – information with far more legal and reputational weight than a typical chatbot prompt. And since meeting assistants have become a standard tool in sales, HR, and project teams across Europe, these questions now reach data protection officers on a regular basis.
This guide explains what "European" actually guarantees in this category, which legal questions come before any vendor comparison, and how to decide between European and non-European tools. It does not rank specific vendors: their processing setups change too often for a static list to stay accurate.
What an AI Meeting Assistant Actually Does
An AI meeting assistant typically combines four functions: live transcription of spoken audio, speaker separation (identifying who said what), automated summarization of the discussion, and extraction of action items or decisions. Many tools also connect to calendars and project management systems, join calls automatically via a bot, and push summaries into other software.
For data protection, the key step is the one between transcription and summarization. Transcription converts audio to text and can run entirely on infrastructure the vendor controls, using speech-recognition models hosted in a specific jurisdiction. Summarization is different. Most vendors send the transcript – sometimes the audio as well – to a large language model (LLM) from a separate company via an API. At that moment, the meeting content leaves the assistant's own systems and enters a second vendor's infrastructure.
Where that second vendor is based, and where its servers run, determines which legal questions apply. That is why "origin" and "hosting" are due-diligence questions, not marketing details.
Why "European" Matters for Meeting Assistants Specifically
Meeting content almost always includes personal data of people who are not the software's customer. A sales call contains a prospect's statements; a recruitment interview contains a candidate's answers; a works council meeting contains employees' positions on sensitive topics. Under GDPR, the organization running the meeting is the controller for this data. That accountability stays with the organization, whichever tool captured the conversation.
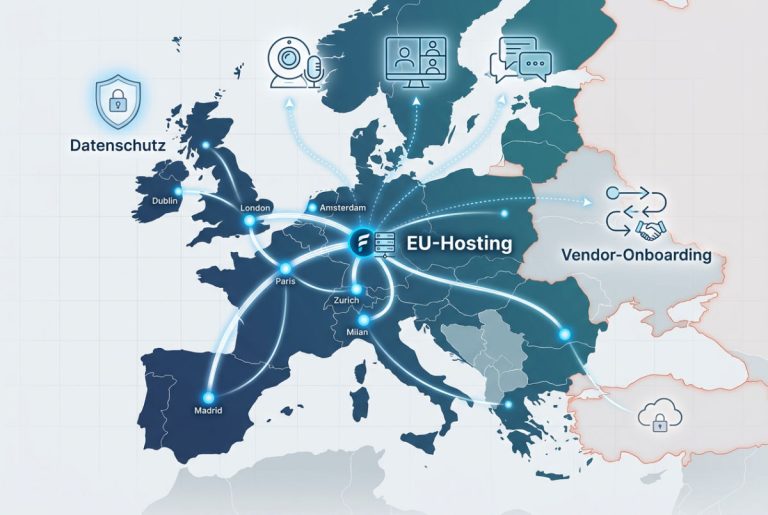
Hosting location matters because of data transfer law. When audio or transcripts are processed outside the EU/EEA, the transfer needs a legal basis under Chapter V of the GDPR. For the United States, two routes are common. Since July 2023, transfers to US companies certified under the EU–US Data Privacy Framework (DPF) can rely on the European Commission's adequacy decision; a vendor's certification can be checked on the official DPF list. For US recipients without certification, Standard Contractual Clauses (SCCs) combined with a transfer impact assessment remain the standard route. Many vendors use both, so the SCCs stay in place as a fallback – the DPF's predecessor, the Privacy Shield, was struck down by the Court of Justice of the EU in 2020.
Neither mechanism changes US government access. Under the CLOUD Act, a US provider can be compelled to disclose data within its possession, custody, or control, even when that data is stored in Frankfurt or Dublin. This applies to the vendor itself and to every US subprocessor in the chain – including the LLM provider that writes the summary.
Marketingtaal vervaagt vaak drie verschillende garanties:
- Europese leverancierHet bedrijf heeft zijn officiële hoofdkantoor in de EU/EER, maar kan de verwerking nog steeds via subverwerkers buiten de EU of LLM API's laten verlopen.
- EU-gehostDe primaire infrastructuur (servers, opslag) bevindt zich in de EU, ongeacht waar het bedrijf is gevestigd.
- Verwerking uitsluitend binnen de EUEr worden op geen enkel moment in het proces persoonsgegevens buiten de EU-infrastructuur verspreid, ook niet via LLM-aanvragen van derden die voor samenvatting worden gebruikt.
Only EU-only processing keeps meeting data within EU infrastructure from start to finish. The first two are useful signals, but on their own they don't tell you where a transcript goes when it is summarized.
Recording Consent Comes Before the Vendor Question
Whichever tool a team chooses, the recording itself needs a legal footing. In Germany, recording the privately spoken word without authorization is a criminal offense under Section 201 of the Criminal Code (StGB). A meeting bot that joins silently and records is therefore a legal risk for the person who deployed it, not a minor compliance detail. Other EU countries have their own rules on recording conversations, and GDPR adds the requirement of a legal basis and clear information for every participant.
In practice, this means announcing the assistant at the start of each meeting, keeping the bot visible in the participant list, giving participants a simple way to object, and documenting how consent or another legal basis is handled. Tools that join automatically via calendar access deserve particular attention, because they can end up in meetings nobody intended to record.
For internal meetings in German companies, the works council also has a say. Section 87(1) no. 6 of the Works Constitution Act (BetrVG) grants co-determination rights over technical systems capable of monitoring employees' performance or behavior – and a tool that attributes every statement to a named speaker falls into that category.
Europese AI-vergaderassistenten versus Amerikaanse alternatieven: vergelijkingscriteria
The table below compares the structural patterns that typically come with each origin, together with the question that settles each point for a specific vendor. The right-hand column carries the most weight: patterns shift when vendors switch LLM providers or add EU regions, while the contract is what binds them.
| Criterium | Typisch patroon: gereedschap van Europese oorsprong | Typisch patroon: tools van Amerikaanse oorsprong met een hostingoptie in de EU. | Wat moet je controleren? |
|---|---|---|---|
| Rechtspersoon / rechtsgebied | Incorporated in an EU/EEA member state; generally outside the CLOUD Act’s direct reach | US parent company, often with an EU subsidiary as contracting party; the parent remains subject to US legal process | Which legal entity signs the DPA, and which company controls it |
| Primaire locatie voor gegevensverwerking | EU-based by default in most cases | EU data region available, sometimes only on higher-tier plans | Where audio, transcripts, and backups are stored – as a contractual commitment, not just a setting |
| Onderliggend LLM voor samenvatting | Either EU-hosted models or a US-based LLM API – both setups exist | Typically a major US foundation-model API | Which LLM provider processes transcripts, in which region, and whether it may use the data for training |
| Transfer mechanism | Not required as long as processing stays in the EU/EEA | DPF certification, SCCs, or both | Certification status on the official DPF list; SCCs included in the DPA |
| Contractuele transparantie (DPA, lijst van subverwerkers) | Depends strongly on company size and maturity | Larger vendors usually publish detailed subprocessor lists | A full, current subprocessor list that names the LLM provider |
A European vendor that sends transcripts to a US LLM API faces the same transfer question as a US vendor – one layer further down the chain. For that reason, the LLM row usually tells you more than the legal-entity row. The binding source for all of it is the vendor's current DPA and subprocessor list, not the marketing page.
Wanneer is een Europese AI-vergaderassistent de betere keuze?
European origin with EU-only processing is the stronger choice in these contexts:
- Juridische praktijken, where client confidentiality obligations extend to any tool that touches case discussions.
- Organisaties die verwant zijn aan de gezondheidszorg, where meetings may reference patient or health information even outside formal clinical records.
- HR- en ondernemingsraadcontexten, where employee data protection rights and co-determination agreements apply directly.
- Overheidsinstanties, which in many EU member states operate under procurement rules that favor or require EU-based processing.
- Organisaties met een bestaand leveranciersbeleid dat uitsluitend EU-leveranciers toelaat., where the decision has already been made at governance level.
Outside these contexts, the summarization LLM decides more than the vendor's nationality. A European company that routes transcripts through a non-EU LLM API without contractual safeguards offers weaker protection than a DPF-certified US vendor with a configured EU data region and a solid GDPR Article 28 DPA.
Voordat een tool wordt gekozen, moet een gedocumenteerde evaluatie het volgende bevestigen:
- waar audio wordt verwerkt, opgeslagen en geback-upt;
- whether the summarization LLM is EU-hosted or an external API, and in which region it runs;
- of een volledige, actuele lijst van subverwerkers is gepubliceerd of op aanvraag beschikbaar is;
- whether retention and deletion periods can be configured to match organizational policy;
- whether the tool offers emotion, sentiment, or engagement scoring based on participants' voices – and whether it can be switched off, since such features are banned in the workplace under the EU AI Act;
- how the tool announces itself to participants and whether automatic joining can be restricted;
- of een ondertekende, aan artikel 28 van de AVG conforme gegevensverwerkingsovereenkomst beschikbaar is vóór de onboarding, en niet pas erna.
When a Non-European Tool Still Makes Sense
A DPF-certified US tool with an EU data region can be a proportionate choice for low-sensitivity internal meetings – team standups or brainstorming sessions without third-party or special-category data. The same applies to organizations already deeply integrated into Microsoft or Google ecosystems, or teams that need language coverage and feature maturity smaller European vendors don't yet offer. The decision weighs what is actually discussed in the meetings against the safeguards a vendor provides. The CLOUD Act exposure remains; for low-sensitivity content, organizations can reasonably accept it as a documented residual risk.
How This Compares to Related European AI Tool Categories
The evaluation logic for meeting assistants overlaps with other European software decisions a B2B team is likely making at the same time. Europese AI-schrijftools raise the same core question – where does the LLM run, and what happens to submitted text – but involve less third-party personal data, since writing tools mostly process content the users wrote themselves rather than statements from external participants.
The video conferencing platform is a dependency worth checking first: some assistants integrate natively through a platform's API, while others join calls as an external bot. That choice affects reliability, how visible the recording is to participants, and which data the platform itself shares with the assistant.
Downstream, meeting summaries and action items usually flow into a CRM or project management system, and recordings often end up in cloud storage. Europese CRM-alternatieven is the relevant reference for teams deciding where sales-call summaries land, and the EU-checklist voor cloudopslag covers the same residency questions for archived recordings and transcripts. Project management tools follow comparable logic. Teams assessing EU AI Act obligations across these AI-assisted workflows can use een kader voor naleving van de EU AI-wetgeving.
Veelgestelde vragen over AI-vergaderassistenten in Europa
Is een Europese AI-vergaderassistent automatisch GDPR-conform?
No. GDPR compliance depends on how data is processed, stored, and secured – and on how the deploying organization informs participants. A European vendor can still fall short if it lacks a proper DPA, uses undisclosed subprocessors, or retains data longer than necessary.
Does a DPF-certified US vendor solve the transfer question?
It provides a valid legal basis for transferring data to that vendor, as long as the certification is active. It does not remove CLOUD Act exposure, and it only covers subprocessors that are themselves certified or bound by SCCs. Keeping SCCs in the DPA as a fallback protects against a future ruling against the framework.
Moeten vergaderassistenten voldoen aan de EU-wetgeving inzake kunstmatige intelligentie?
It depends on the features. Inferring employees' emotions from their voice – sometimes marketed as sentiment or engagement analysis – falls under the ban on emotion recognition in the workplace in Article 5, which has applied since February 2025, apart from narrow medical and safety exceptions. Standard transcription and summarization are not prohibited; deploying organizations should still document which features are active. See richtlijnen voor naleving van de EU AI-wetgeving met betrekking tot software for a detailed framework.
Kunnen vergaderingsopnames worden verwerkt zonder de audio naar een externe LLM-provider te sturen?
Yes, if the vendor runs its own speech-recognition and summarization models on infrastructure it controls. Ask for this in writing, since many vendors – including European ones – rely on third-party APIs for the summarization step.
Wat moet er gecontroleerd worden voordat een vergaderassistent toegang krijgt tot een agenda?
The scope of permissions requested (read-only versus full access), whether the tool joins every meeting automatically or only when invited, and what happens to calendar metadata. Attendee names and meeting subjects are personal data in their own right, even without a recording.
Worden opnames na verwerking automatisch verwijderd?
That depends on vendor and plan. Some offer configurable retention periods or automatic deletion after a set time; others keep recordings indefinitely by default. Set retention explicitly during onboarding instead of relying on the default.
Belangrijkste conclusies
The decisive question for AI meeting assistants is where audio and transcripts are processed – above all, which LLM writes the summary and where it runs. Vendor nationality is a starting point; the DPA, the subprocessor list, and the transfer mechanism show what is actually guaranteed.
Two questions come before any vendor comparison: how participants are informed about the recording, and whether the works council needs to be involved. Teams that settle these first and then request DPAs, subprocessor lists, and processing-location details directly from vendors make a decision they can defend – independent of "GDPR-compliant" or "European" marketing claims.